HSM-backed key management uses a hardware security module as the tamper-resistant root of trust for cryptographic keys, generating and storing them so they never leave the device in plaintext. The core recommendation for most organizations: reserve HSMs for root and other high-assurance keys, then pair the module with a key management service to handle rotation, policy, and lifecycle. Before committing budget, verify FIPS validation status and CMVP listing rather than taking a vendor’s marketing claim at face value.
TL;DR:
- HSMs should be used primarily for root, CA, and high-assurance keys, with their FIPS validation status and CMVP listing verified before procurement.
- Both physical and cloud HSMs generate keys inside their hardware boundary, ensuring private keys never leave in plaintext, and integration standards like PKCS#11 and KMIP must be supported.
- Operational best practices include generating keys within the module, defining short cryptoperiods, separating roles, and testing key backup and destruction procedures prior to go-live.
- On-premises HSMs offer full control but require extensive capacity planning, while cloud and multi-tenant models reduce operational overhead at the cost of some control.
- An HSM investment is strategic when handling critical data or signing keys, but organizations should first address operational gaps in their key management before deploying hardware security modules.
What an HSM is and the security guarantees it provides
An HSM is a dedicated physical or cloud-hosted device built to generate, store, and use cryptographic keys inside a hardware boundary that resists physical and logical tampering. A physical HSM sits in a data center or is rack-mounted under the organization’s control; a cloud HSM runs the same validated hardware inside a provider’s infrastructure, single-tenant or multi-tenant depending on the service.
The core guarantee is non-exportability: private keys are generated inside the module and never leave it in usable form, so a compromised application server or a stolen backup cannot expose the raw key material. Operations happen inside the boundary; only the signed, encrypted, or wrapped output crosses to the requesting system.
Before trusting any HSM claim, verify:
- FIPS 140-2 or FIPS 140-3 validation, confirmed against NIST’s key management guidelines rather than a vendor data sheet
- CMVP listing showing the specific module and firmware version, not just the product family
- Common Criteria certification, where the deployment requires it for procurement or regulatory reasons
When to choose an HSM vs. software-only KMS
The decision hinges on what happens if a key leaks and how much operational overhead the team can absorb. Certain use cases justify hardware protection regardless of cost:
- Code signing, where CA/Browser Forum rules commonly require non-exportable private key storage
- PKI root and intermediate certificate authority keys
- Payment processing and cardholder data encryption keys
- Regulated data subject to sector-specific compliance mandates
A managed, software-only KMS is acceptable for most application-level encryption, internal service-to-service secrets, and workloads where the provider’s shared responsibility model already meets the organization’s risk tolerance. The trade-off is operational: dedicated HSMs cost more and demand real staffing, while a multi-tenant KMS trades some control-plane independence for lower overhead, a point vendor guidance on the HSM and KMS stack makes directly.
Pro Tip: Map each key to its worst-case compromise scenario before choosing a storage tier: a leaked session key is an incident, a leaked root signing key is an organizational crisis.
How HSMs integrate with KMS and applications
Treat the KMS and the HSM as two distinct layers with different jobs. The KMS handles lifecycle: policy, rotation schedules, access grants, audit logging, and API exposure to applications. The HSM handles the cryptographic operation itself: key generation, signing, encryption, and decryption inside its hardware boundary. Confusing the two leads to designs that either bypass hardware protection or overload the HSM with tasks it was never built to do.
When evaluating compatibility, check these in order:
- Interface support, since PKCS#11 and KMIP remain the most widely implemented standards for HSM integration, alongside platform-specific providers like CNG, JCE, or OpenSSL engines
- BYOK and import paths, confirming the HSM supports secure key wrapping during transport so imported keys never touch plaintext outside the module
- Export controls at the KMS layer, verifying the KMS enforces the same non-exportability rules the HSM guarantees, rather than quietly allowing a plaintext export path
Key lifecycle best practices for HSM-backed keys
NIST SP 800-57 sets the baseline: generate keys inside FIPS-validated modules, never allow plaintext export, and maintain a documented compromise-recovery plan alongside enforced separation of duties. Those three requirements should shape every operational runbook a team writes for HSM-backed keys.
- Generate inside the module. Keys created outside the HSM and imported later carry the risk of having existed in plaintext somewhere first.
- Define cryptoperiods and automate rotation. A shorter cryptoperiod limits the blast radius of an undetected compromise, and automation removes the human delay that turns a policy into a suggestion.
- Separate duties by role. The person who manages key metadata should not be the same person who can invoke cryptographic operations on a high-assurance key.
- Back up through wrapped exports or a recovery server, never through a plaintext copy, and test the restore path before it becomes an emergency.
- Verify before destruction. Confirm no active dependency references a key before it is zeroized.
NIST SP 800-57 mandates that cryptographic keys be generated within FIPS-validated cryptographic modules, which makes module validation status a gating requirement, not a nice-to-have, for any HSM procurement decision.
Deployment models and operational considerations
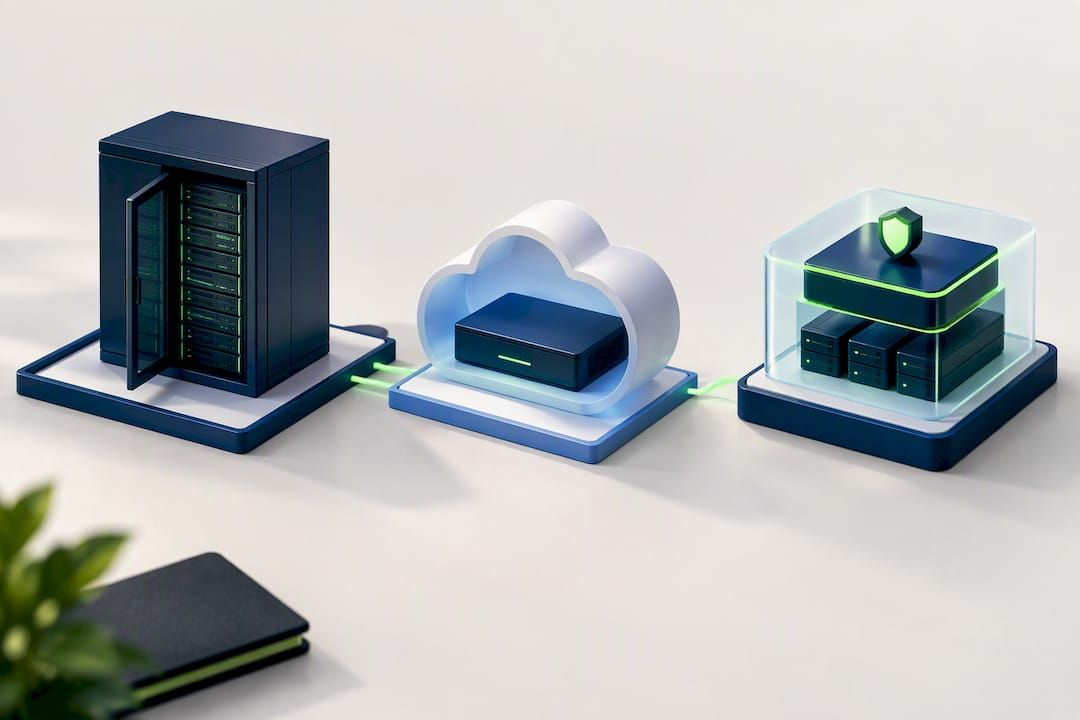
Three deployment shapes cover most enterprise scenarios, and each shifts cost and control differently. On-prem dedicated HSMs give full control over physical access and firmware but require the organization to own capacity planning, patching, and disaster recovery entirely. Dedicated cloud HSM instances keep single-tenant hardware isolation while offloading physical maintenance to the provider. Multi-tenant KMS with HSM backing behind it minimizes operational burden but relocates some control-plane visibility into the vendor relationship.
Capacity planning matters more than most teams expect. Peak cryptographic throughput should be measured by workload type, since TLS handshake volume behaves very differently from batch signing operations, and HSMs typically scale by adding instances rather than through the elastic autoscaling common to multi-tenant KMS offerings.
During procurement, raise these questions directly with any vendor:
- What FIPS level does the module carry, and can you provide the current CMVP certificate number?
- Which interfaces are supported natively, and which require a middleware layer?
- What SLA governs HSM availability, and what is the documented failover behavior during an outage?
Steps to plan, install, and go live with HSM-backed keys
A disciplined rollout follows four phases, each building on the last.
- Plan. Inventory every key currently in use, classify each by threat model, and decide which certifications the deployment actually requires rather than defaulting to the highest tier available.
- Install. Deploy the HSM client or software agent on the KMS or vault servers that will call it, and establish encrypted, authenticated connectivity between them.
- Enroll. Register the KMS as a recognized HSM client, generate a small batch of test keys to validate generation and audit logging before touching production traffic.
- Go live. Run a rotation cycle end to end, confirm the backup and recovery path actually restores a usable key, and rehearse the incident procedure for a suspected compromise before it happens for real.
Pro Tip: Rehearse key destruction on a throwaway test key before the first production destruction; the procedure that looks simple on paper often surfaces a dependency nobody documented.
Practical lessons from implementation
Recurring pattern across HSM deployments: teams treat the module as set-and-forget once it passes initial testing, then discover lifecycle gaps months later when a rotation deadline is missed or a role has broader access than intended. Pairing the HSM with a KMS that enforces rotation schedules and role granularity closes most of that gap. Readers building the encryption-at-rest layer around HSM-protected keys can walk through the envelope encryption and backup patterns that make this concrete, and the same modular delivery approach behind Bitecode’s 90-day golden record project applies directly to HSM integration timelines.
When an HSM investment is strategic versus tactical
An HSM is strategic when regulated data, code signing, or payment keys are already in production and a compromise would be existential, not merely embarrassing. It is tactical, and often premature, when a team lacks the staffing to run rotation, monitoring, and incident response consistently. Fix operational KMS gaps first; hardware without discipline behind it buys little.
— Bitecode
Building HSM-backed systems without the long build cycle
A modular delivery model that starts projects with a meaningful share of the baseline system already built can shorten the path from architecture decision to a working HSM-integrated KMS. That matters most for custom business software and advanced cloud applications where secure key handling has to sit correctly inside a larger financial or automation workflow, not bolted on afterward.
Teams weighing an HSM-backed KMS project can bring their key inventory and threat model to Bitecode’s main services page to scope the build.
Authority sources and standards to read next
- NIST SP 800-57, Part 2: the core federal recommendation for cryptographic key management
- NIST key management guidelines: the consolidated CSRC project page covering all three parts of SP 800-57
- NSA/CISA cloud key management guidance: defense-sector best practices for HSM use in cloud workloads
- OWASP Key Management Cheat Sheet: developer-focused operational controls for key storage
FAQ
What is HSM in key management?
An HSM, or hardware security module, is a dedicated device that generates and stores cryptographic keys inside a tamper-resistant hardware boundary so they never exist in plaintext outside it. In key management, it acts as the root of trust, while a separate KMS layer typically handles rotation, policy, and lifecycle around the keys the HSM protects.
Is Yubikey a HSM?
A YubiKey is a hardware authentication token, not an HSM, since it is designed for user authentication and small-scale credential storage rather than enterprise-grade key generation and cryptographic processing at scale. HSMs undergo formal validation such as FIPS 140-2 or 140-3 for exactly this kind of high-throughput, high-assurance use.
What’s the difference between TPM and HSM?
A TPM, or trusted platform module, is a low-cost chip built into a device to secure that specific device’s boot process and local credentials, while an HSM is a dedicated, often removable or networked module built to serve cryptographic operations to multiple applications or systems at enterprise scale. HSMs also carry formal certifications like CMVP listing that TPMs generally do not pursue for the same purpose.
What is key management?
Key management is the set of processes covering how cryptographic keys are generated, distributed, stored, rotated, and eventually destroyed throughout their operational life. NIST SP 800-57 frames this as requiring validated generation, defined cryptoperiods, and documented recovery plans rather than ad hoc handling.