Data residency controls ensure designated data and its backups remain and are processed only in approved geographies, enforced through region restrictions, customer-managed keys, and continuous monitoring. Guidance from NIST and CISA’s TIC program points toward identity-based, policy-as-code enforcement rather than static network rules, and that approach is the practical starting point. Teams should inventory regulated data, deploy enforcement before storage provisioning, and enable continuous audit logging from day one.
TL;DR:
- Residency programs must include backups, disaster recovery replicas, and metadata to avoid gaps during audits, not just primary data storage.
- Contractual region commitments do not guarantee that all services, such as support or logging, respect geographic boundaries, especially under multi-cloud environments.
- Enforcement should utilize multi-layer controls, including locality policies, customer-managed encryption keys, and confidential computing, with policy-as-code to ensure compliance.
- Continuous monitoring and immutable audit logs of cross-region access, key usage, and policy changes are essential to demonstrate compliance during audits.
- Ownership of residency policies must involve cross-functional teams, as policies are living documents that require ongoing governance to prevent drift and inadvertent violations.
1. What counts as data for residency controls
Residency programs fail most often because teams scope them too narrowly. A policy that governs only the primary database while ignoring backups, disaster recovery replicas, and metadata is not a residency control, it is a gap waiting to surface in an audit.
A complete scope includes:
- Primary data stores: the production databases, object storage, and file systems holding regulated records.
- Backups and snapshots: copies that often replicate to different regions by default under standard retention policies.
- Disaster recovery replicas: secondary environments that must honor the same geographic boundaries as production.
- Metadata and logs: indexing, search, and telemetry systems that can inadvertently store identifiable fragments outside the approved region.
- Processing locations: where compute actually executes, which is not always the same region as where data is stored at rest.
Contractual residency, the commitment a cloud provider makes in a data processing agreement, is not the same as legal residency, the obligation a statute or regulator imposes. A vendor can promise regional storage while a global support or logging service still touches the data outside that boundary. This is the most common misunderstanding IT teams run into: selecting a region in a console does not guarantee every dependent service, from content delivery caching to anomaly detection, respects that same boundary. Each provider publishes which services are regional and which are global, and that distinction belongs in the system security plan, not just the architecture diagram.
2. Laws and compliance drivers that create residency obligations
Residency requirements rarely originate from a single law. They accumulate from overlapping statutes, sector rules, and contract language, and compliance teams need a working map rather than a deep dive into any one regime.
The CLOUD Act gives US authorities a legal basis to compel data production from providers under US jurisdiction, regardless of where the data physically sits. That reach persists even when a workload is hosted in a foreign region, which means geographic storage alone does not resolve every sovereignty concern for organizations using US-headquartered cloud providers.
GDPR adds a second layer for organizations handling data tied to the European Economic Area. Cross-border transfers typically rely on Standard Contractual Clauses or Binding Corporate Rules, and both require documented technical and organizational measures, not just a signed clause. A residency control without supporting encryption and access logging will not satisfy a regulator reviewing a transfer impact assessment.
Sector rules layer on top of these general frameworks:
- HIPAA governs protected health information and requires business associate agreements that often specify storage and processing boundaries.
- ITAR restricts technical data related to defense articles to US persons and, in many cases, US soil, with no tolerance for incidental foreign access.
- FedRAMP sets authorization baselines for cloud services used by federal agencies, including residency and personnel vetting requirements.
Before signing or renewing any cloud contract, compliance teams should verify: which regions the provider commits to in writing, whether that commitment extends to backups and support access, how subprocessors are disclosed, and what breach notification timelines apply. Microsoft’s own sovereign controls documentation is explicit that some services replicate or move data even when a regional deployment is selected, so the DPA review has to cover service-by-service behavior, not just the headline region commitment.
NIST IR 8613 notes that multi-cloud environments introduce geographic data blind spots and synchronization complexity for keys and backups across integrated providers, which is precisely the failure mode a contract review is meant to catch before it becomes an incident.
3. Residency vs sovereignty vs localization: operational framing
These three terms get used interchangeably, and that imprecision causes real implementation errors.
Data residency simply means data is stored and processed within a chosen geographic boundary. Data sovereignty goes further: it means the data is subject to the laws of the country where it resides, and often requires that the provider’s own operational, administrative, and legal reach stay confined to that jurisdiction too. Data localization is a legal mandate, usually statutory, requiring that certain data categories never leave a country’s borders at all.
An organization satisfying residency alone might store data in the right region while a provider’s global support staff, headquartered elsewhere, still has technical access to it. Sovereignty demands closing that gap: restricting support personnel by citizenship or location, controlling where encryption keys are generated and held, and sometimes requiring in-country legal entities to operate the infrastructure.
- Residency is a geography question: where does the data sit?
- Sovereignty is a jurisdiction question: whose laws and personnel can touch it?
- Localization is a legal mandate question: does a statute forbid the data from leaving at all?
The operational consequence shows up first in key management and support access policies, both of which need separate review from the storage architecture diagram.
4. Three-level technical control framework: locality, CMKs, and confidential computing
Microsoft’s sovereign controls guidance organizes residency enforcement into three levels that map cleanly onto a prioritization framework any team can use regardless of cloud provider.
Level 1: Enforce locality and encrypt in transit. This is the baseline: region-deny policies that block resource creation outside approved geographies, combined with transport encryption for all data in motion. It is the easiest to implement and the first thing an auditor will check, since it can be verified through control-plane configuration alone.
Level 2: Encryption at rest with customer-managed keys. CMKs give the organization, not the provider, control over the key lifecycle. This matters legally as much as technically: if a government request reaches the provider but the organization holds the only copy of the key, the provider cannot produce decrypted data without the customer’s cooperation. The trade-off is operational complexity, since key rotation, backup, and regional key-store placement all become the organization’s responsibility rather than the provider’s.
Level 3: Confidential computing and encryption in use. This level protects data while it is actively being processed in memory, using hardware-based trusted execution environments. It is rarely required outside the most sensitive workloads, financial transaction processing, defense-related data, or health records under strict sector mandates, but where it is required, no lower level substitutes for it.
Policy-as-code is what makes each level enforceable rather than aspirational:
- Level 1 maps to region-deny rules in tools like AWS Config or Azure Policy, checked at deployment time.
- Level 2 maps to KMS or Key Vault policies that restrict key usage by region and require customer-managed key references on every storage resource.
- Level 3 maps to attestation checks that verify workloads are running inside a trusted execution environment before granting data access.
The NCCoE’s trusted compute pools practice guide demonstrates that hardware attestation provides stronger evidence of workload locality than administrative region selection alone, which is the reason Level 3 exists for workloads where a regulator or counterparty needs proof, not just a configuration setting.
Pro Tip: Treat Level 2 as the default for any data covered by a DPA with a region clause. The operational overhead of CMKs is lower than the legal exposure of relying on provider-managed keys alone.
5. Operational playbook: step-by-step implementation of residency controls
Residency programs succeed when they follow a fixed sequence rather than ad hoc fixes applied after an audit finding. The order matters because each step depends on information the previous one produces.
- Inventory and classify data by regulation and sensitivity, tagging each dataset with the laws that apply to it (GDPR, HIPAA, ITAR, FedRAMP, or none).
- Map every data flow, including backups, DR replicas, and metadata stores, to find blind spots before they become findings. NIST IR 8613 identifies exactly this kind of mapping gap as a recurring challenge in multi-cloud environments.
- Codify residency as policy-as-code, writing region-deny and service-restriction rules into the deployment pipeline so violations are blocked before provisioning, not caught after the fact.
- Decide key management architecture, choosing where CMKs are generated, how they rotate, and which regional key stores hold them for each sensitivity tier.
- Deploy continuous monitoring, logging cross-region access attempts, key usage events, and policy changes to an append-only store that auditors can query independently.
- Document everything in a system security plan that ties each control back to the regulation it satisfies, since auditors evaluate evidence, not intentions.
Internal engineering guides on at-rest encryption, key management, and backup handling are a useful reference when step four turns into a cross-team key rotation project.
Pro Tip: Run the data flow mapping exercise before writing a single policy-as-code rule. Teams that write enforcement first routinely discover a backup job or logging pipeline the policy never covered.
6. Architecture and policy-as-code patterns for survivable residency enforcement
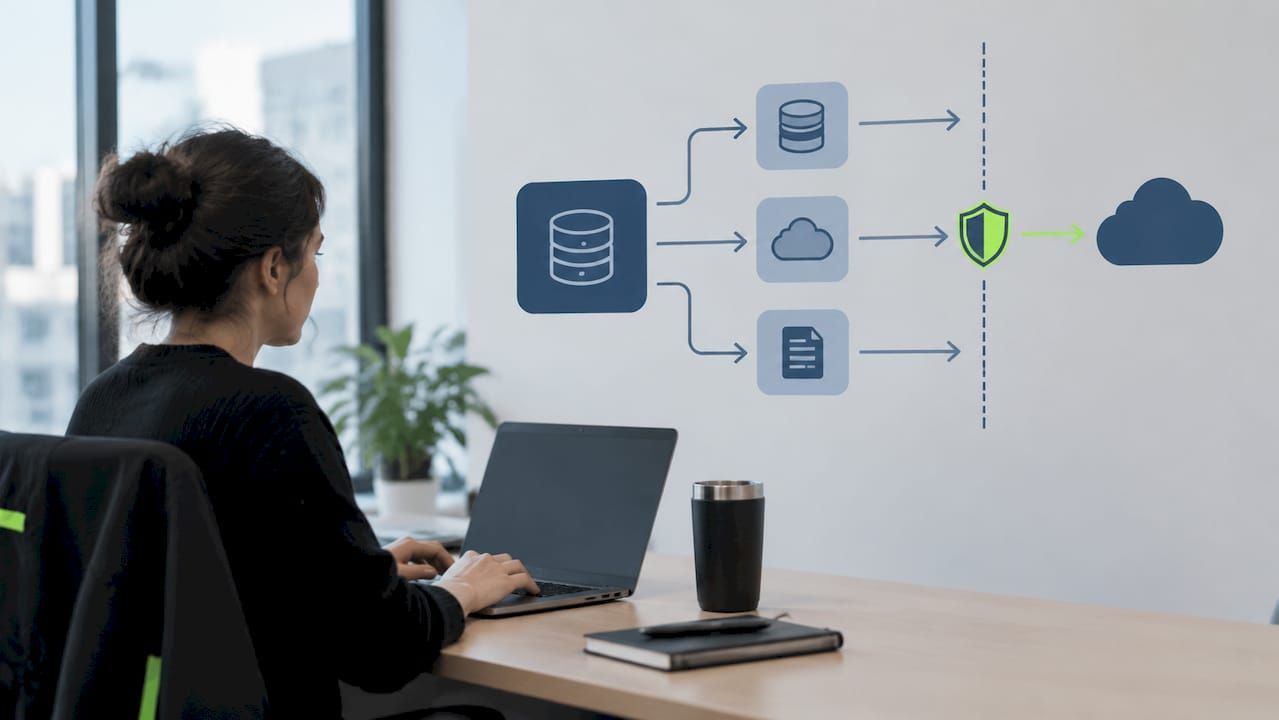
Enforcement that lives only in documentation does not survive a platform migration, a new engineer’s deployment script, or a vendor’s product update. It has to live in the stack itself, at points the architecture calls policy enforcement points, or PEPs.
CISA’s TIC 3.0 reference architecture recommends distributing enforcement across multiple PEPs, chaining checks at the network edge, the API gateway, and the workload itself, rather than relying on a single chokepoint that can be bypassed or misconfigured.
- Edge PEPs block traffic to unapproved regions before it reaches application infrastructure.
- API gateway PEPs enforce service-level policies, checking that a request’s data classification matches the region it is about to touch.
- Workload-level PEPs, often implemented through a service mesh, verify the identity of the calling service before granting access to regional resources.
NIST SP 800-207A pushes this further by recommending identity-based enforcement over network-based rules entirely. Application identities using standards like SPIFFE, short-lived tokens, and multi-tier policies enforced through service meshes or policy engines survive workload mobility in a way IP-based firewall rules do not. A workload that moves between availability zones or gets rescheduled by an orchestrator keeps its identity-based policy intact, while a network rule tied to a subnet range breaks immediately.
Observability closes the loop. Without attestations and telemetry tying actual data movement back to the approved policy, a residency program is a set of rules nobody can prove were followed. Signed attestations from the workload, combined with access logs tied to service identity rather than IP address, give auditors a verifiable chain rather than a configuration screenshot.
7. Audit readiness and continuous monitoring: evidence you must collect
Auditors do not accept intent. They accept evidence, and the evidence has to be continuous, not reconstructed after the fact.
The telemetry that matters most:
- Cross-region access logs, showing every attempt to read or write data outside the approved boundary, successful or blocked.
- KMS key usage records, documenting every decryption event tied to a specific CMK and the identity that triggered it.
- Policy-as-code change logs, capturing who modified a region-deny rule or key restriction and when.
Evidence only holds up when it is immutable. Append-only logging, signed attestations from workloads, and CMK audit trails that cannot be edited after the fact are what separate a defensible audit package from a spreadsheet assembled the week before a review. AWS’s own guardrail model, built around Control Tower, Config rules, and control-plane logging, follows this same principle: prevention first, detection second, and an unalterable record third.
Policy drift and unauthorized transfer attempts are the two KPIs that matter most for an ongoing program, and both should be reviewed on a fixed cadence rather than only when a contract renewal or audit forces the question. A quarterly review of policy-as-code diffs, paired with monthly review of flagged cross-region access attempts, catches drift before it becomes a finding. Checklist-style internal processes, like the kind outlined in a SaaS security compliance checklist, help standardize that cadence across teams that otherwise treat audit prep as a once-a-year scramble.
8. Bitecode practitioner view: integrating residency controls into custom enterprise software
Cloud-native residency controls cover the infrastructure layer well, but gaps persist at the application and workflow layer, particularly where financial processing, custom audit dashboards, or blockchain modules sit on top of standard cloud services. Custom enterprise software projects can include integrations such as CMK orchestration tied to application-level data classification, policy-as-code pipelines deployed alongside business logic, and audit dashboards that pull evidence from multiple providers into a single view. The value sits in closing the gap NIST IR 8613 describes between provider-level controls and the organization’s own compliance obligations, through automation rather than manual reconciliation.
9. Why residency needs continuous governance and cross-functional ownership
The conventional view treats residency as an infrastructure problem engineering solves once and audits rubber-stamp afterward. That view is wrong, and it is why so many programs drift out of compliance within a year of passing their first audit.
Residency is a living policy, not a one-time deployment. Legal teams change contract terms, procurement adds new vendors with different regional footprints, and engineering ships features that quietly introduce new data flows. Without a standing governance group spanning legal, security, procurement, and engineering, the policy-as-code rules written at launch become stale, and nobody notices until an auditor does. The real cost is not the maintenance effort, it is the risk of discovering the gap during a regulator’s inquiry instead of a routine review.
— Bitecode
10. How Bitecode helps you put these controls into production
Implementing the framework above, region enforcement, CMK orchestration, continuous audit logging, takes real engineering time most compliance teams do not have in-house. Bitecode builds this as custom software: automation workflows that enforce policy-as-code at deployment, financial and audit modules that generate evidence streams automatically, and cloud integrations that unify monitoring across providers instead of leaving teams to reconcile logs by hand.
The outcome is a residency program with audit-ready documentation and far less manual reconciliation work. Start with a scoped project through Bitecode’s custom business software services and build enforcement around the data flows your organization actually has.
Sources
FAQ
What does “data residency” mean?
Data residency means data is stored and processed only within a specific geographic boundary, such as a country or region, that an organization or regulation requires. It covers primary storage, backups, and processing locations, though not every cloud service honors that boundary by default, so each service needs separate verification.
What are the 7 DPA principles?
Definitions of “DPA principles” vary across frameworks and contracts, so there is no single universal list of seven. In practice, data processing agreements commonly address purpose limitation, security measures, subprocessor disclosure, breach notification, data location commitments, audit rights, and deletion obligations, and each should be verified against the specific agreement in use.
Is GDPR still a thing?
Yes, GDPR remains in force and continues to govern data tied to the European Economic Area, including cross-border transfer requirements through Standard Contractual Clauses or Binding Corporate Rules. Organizations handling EEA-linked data still need documented technical and organizational measures to satisfy it.
What are some examples of data controls?
Common technical controls include region-deny policies that block deployment outside approved geographies, customer-managed encryption keys, geo-conditional identity and access management rules, and confidential computing for data actively being processed. Monitoring controls like cross-region access logging and policy-as-code change tracking complete the picture by providing audit evidence.
How do residency controls differ across multi-cloud environments?
Multi-cloud setups introduce synchronization challenges for key management and audit logging because each provider handles regional commitments and global services differently. Bespoke middleware or managed integration work is often needed to present a single consistent audit view across providers.